 Supabase
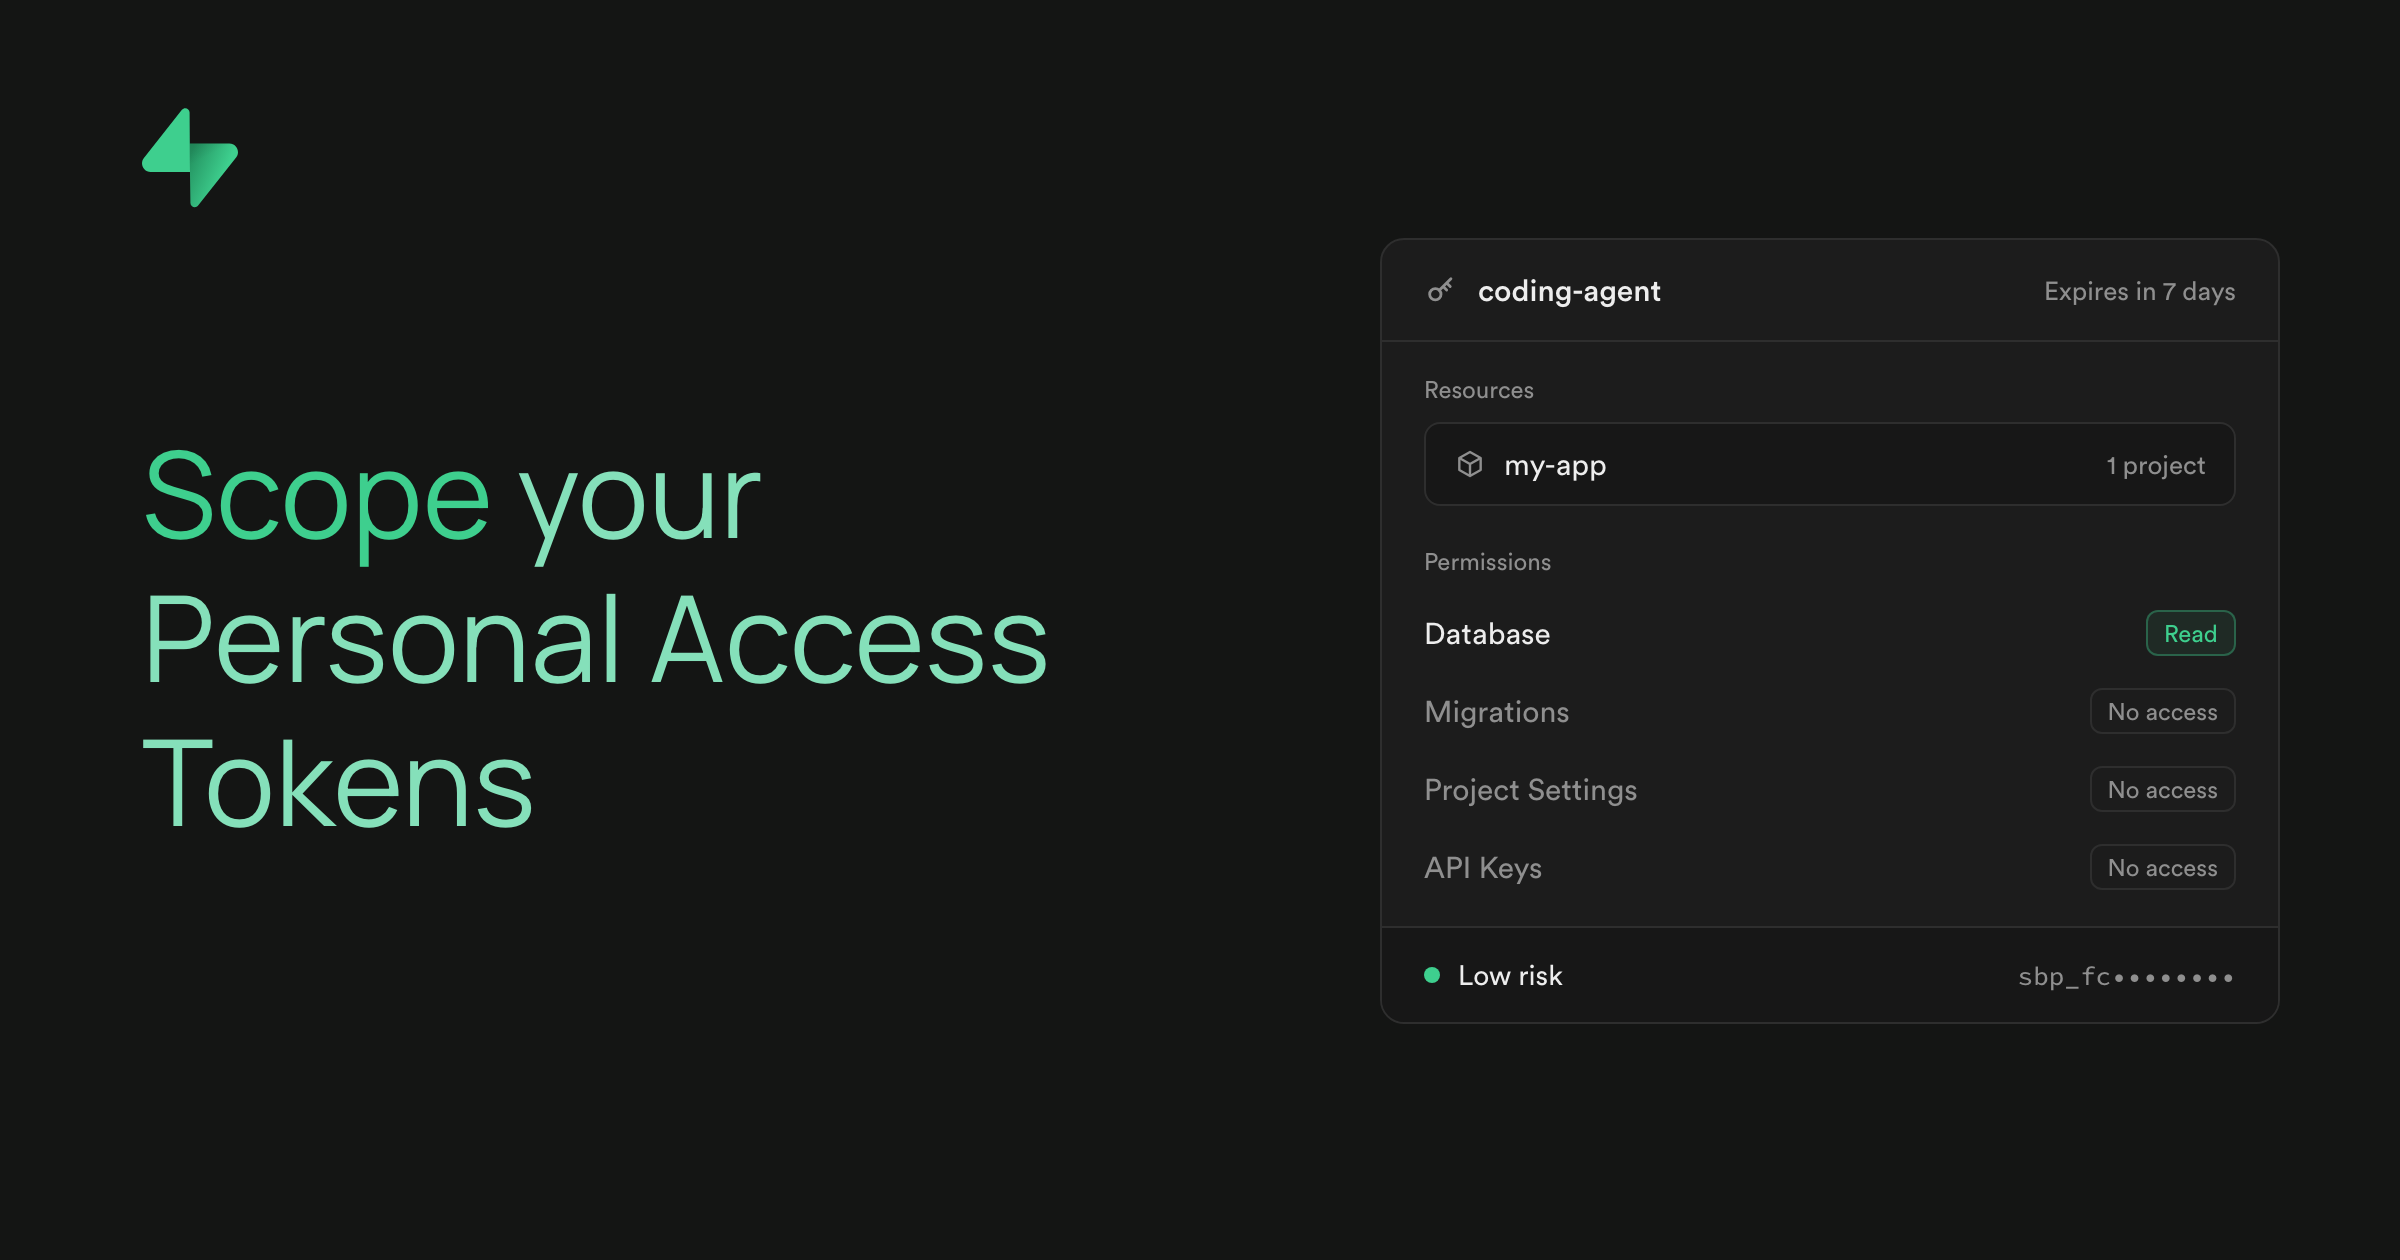
Scoped Personal Access Tokens now let Supabase users restrict a credential to specific organisations, projects and permissions. New tokens created in the Dashboard use scoping by default.
Previously, a Personal Access Token could do anything its owner could do across every organisation and project in their account. A CI pipeline, deployment script or coding agent given that token inherited the same broad access.
According to the Supabase blog post, token scoping became generally available on 28 September 2026 and was announced at Supabase Select on 2 October. Nearly nine out of 10 tokens created through the Dashboard since launch have been scoped.
How Scoped Personal Access Tokens Work
When creating a token, users first choose which resources it can reach. A token can cover multiple organisations, although the Dashboard recommends project-level access.
Permissions are then set for the selected resources. Three presets are available: No access, Read-only and Full access. Individual permissions can also be toggled, allowing a token to read database information without receiving write access or access to unrelated resources.
Read-only is broader than database access alone. It includes secrets such as API keys, so Supabase recommends starting with No access and enabling only the required read permissions.
- 1
Choose resources
select the organisations or individual projects the token can access
- 2
Set permissions
apply a preset or toggle each required permission
- 3
Add an expiry
choose how long the credential should remain valid, up to one year
- 4
Review the risk
check the access summary and risk rating before creating the token
The Dashboard displays a risk banner showing the token's potential blast radius. Its permissions also remain bounded by the user's own role, so a token cannot grant access its owner does not have.
Separate Credentials for Separate Jobs
A coding agent that inspects tables, generates types and runs read-only SQL can now receive a token limited to one project and database reads. A deployment script can use a different token containing the write permissions needed for its workflow.
Full-account tokens remain available when required. The default creation flow now directs users towards narrower credentials instead. This also complements Supabase's work on giving each coding agent its own local project.
Frequently asked questions
What are Supabase Scoped Personal Access Tokens?
They are credentials restricted to selected organisations, projects and permissions. They can also expire after a chosen period of up to one year, while their access remains limited by the owner's role.
When are Scoped Personal Access Tokens available?
They became generally available on 28 September 2026. Scoping is now the default for new tokens created in the Dashboard, although full-account access can still be selected.
Which Supabase plan includes Scoped Personal Access Tokens?
The blog post does not list plan restrictions. Scoped tokens are created from the account access tokens page in the Dashboard.
Sources
3 checkedHow we cover tool news: Create With's tool desk drafts these reports with AI from the sources listed above and checks them against those sources before publishing.





 ElevenLabs