 Vercel
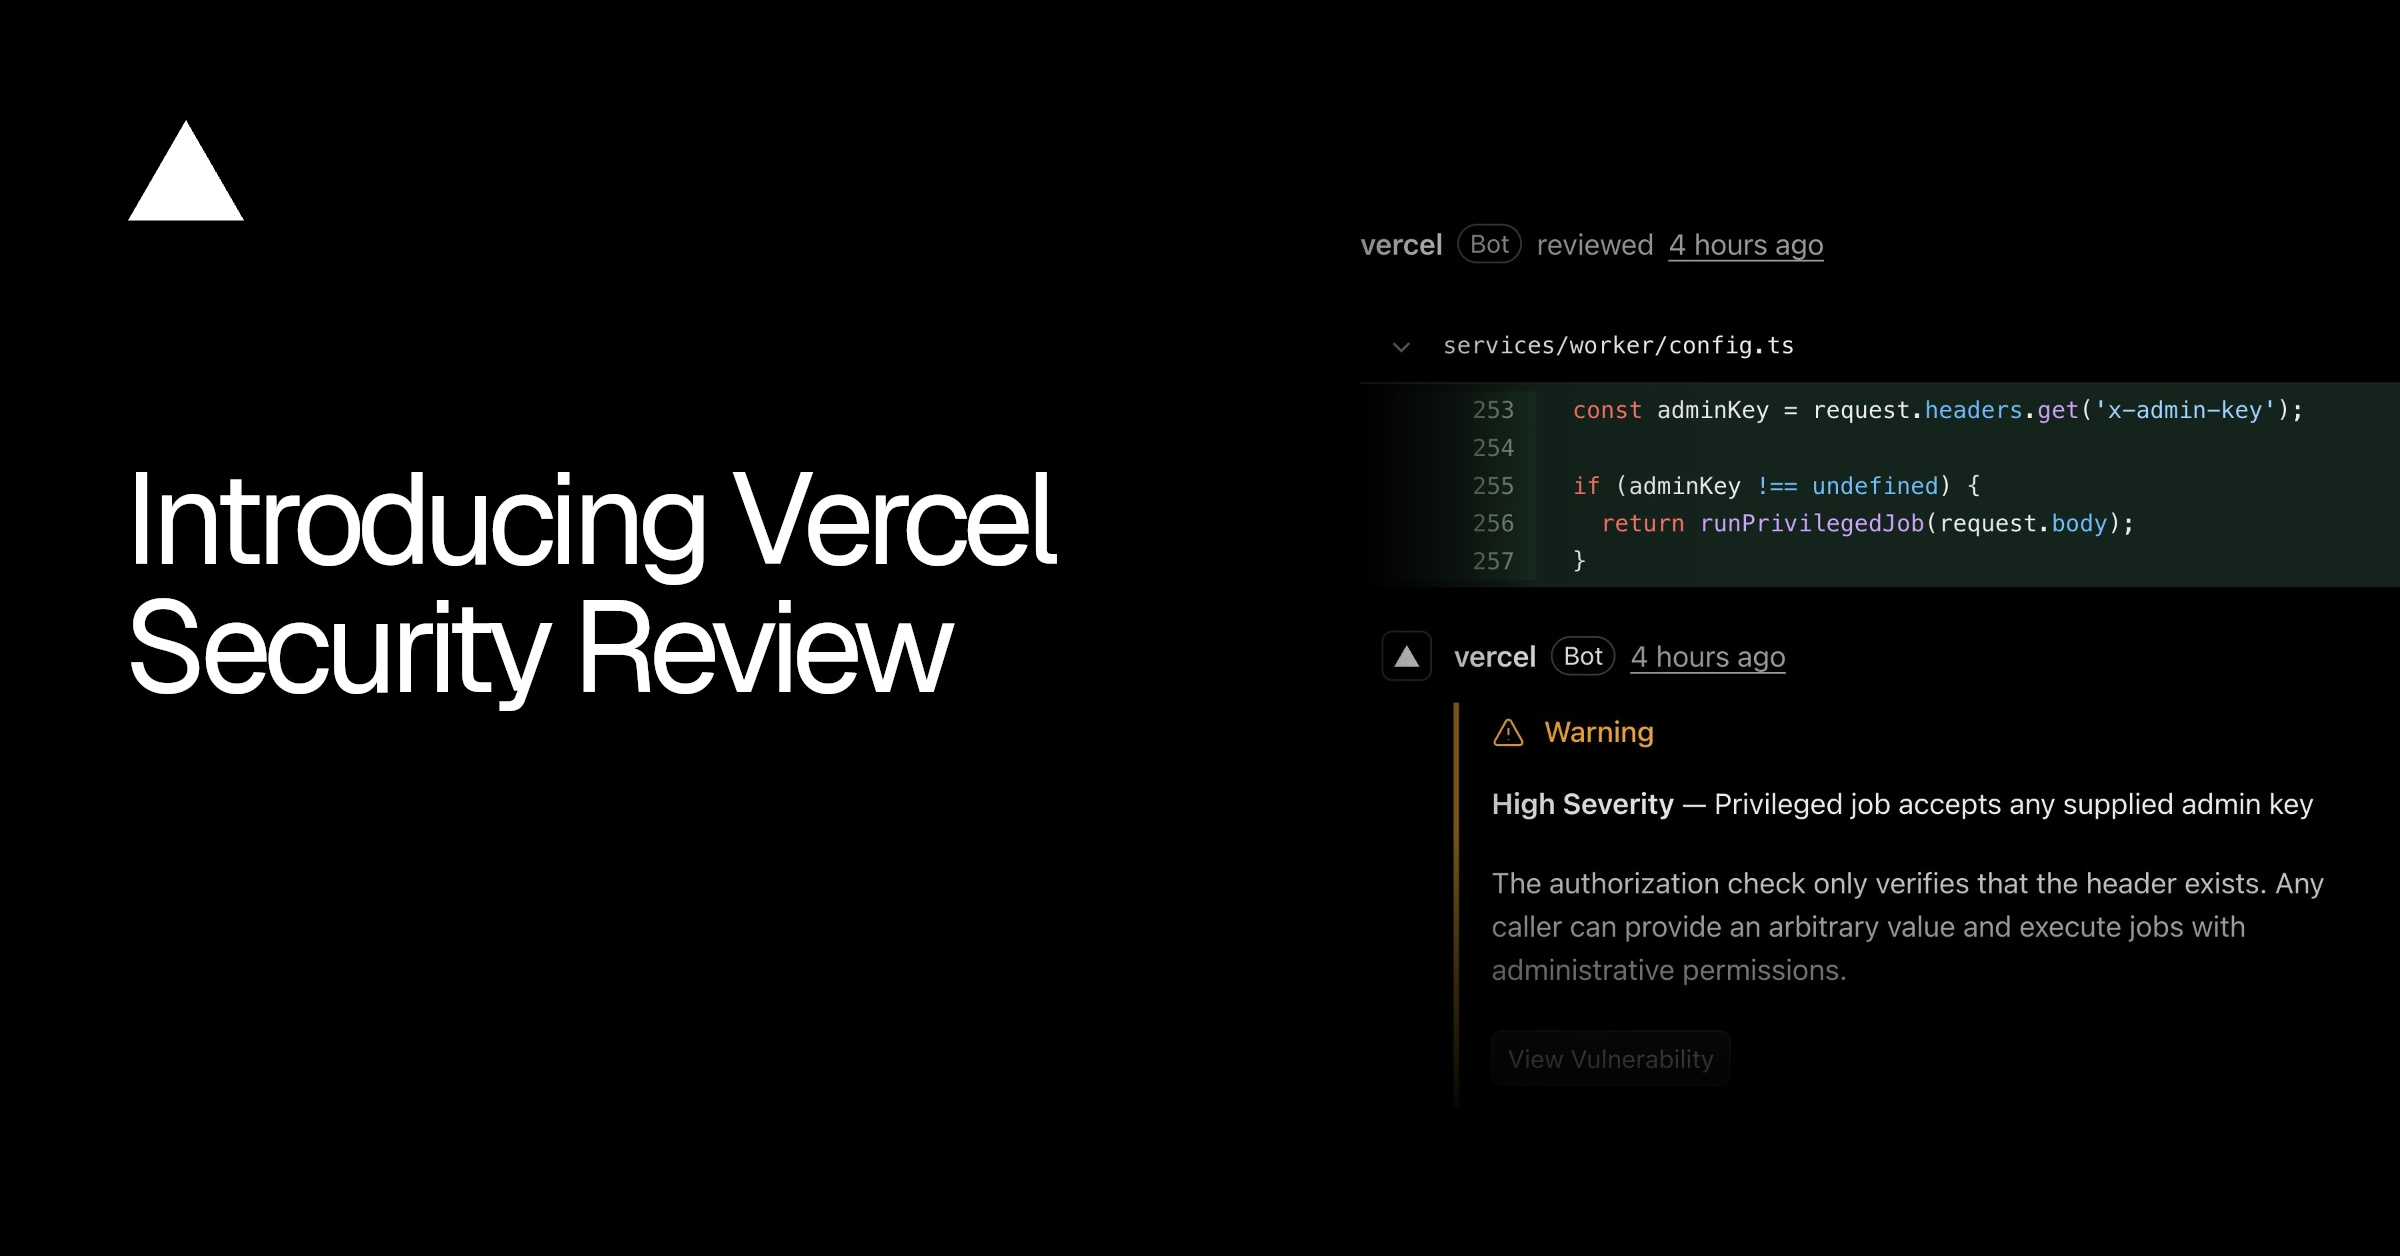
Vercel Security Review automatically scans every push to a connected GitHub repository for vulnerabilities.
Once enabled, it runs when GitHub receives a push rather than waiting for a pull request. That means direct and force pushes to a production branch are covered too. If one push affects several projects, Security Review examines them together.
The launch blog places Security Review alongside Vercel Agent’s existing Code Review and Investigation capabilities. It follows Vercel’s recent work to block malicious npm packages during builds.
How Vercel Security Review Reports Vulnerabilities
Each finding includes the affected project, environment, branch and commit. It also contains a summary, a suggested fix and an AI-generated severity rating.
Developers can see findings in three places:
- Pull request review comments
- The Vulnerabilities area of the Security dashboard
- The command-line interface
Security Review also creates its own GitHub check. With the user’s permission, Vercel Agent can validate a suggested fix and push the change. The review itself remains tied to the push event, so it can catch changes that bypass a normal pull request workflow.
In monorepos, each review is scoped to the project’s root directory. This keeps the scan focused on the code belonging to that Vercel project while allowing all projects affected by one push to be reviewed.
Where It Fits in a Deployment Workflow
The public beta changelog confirms that teams must enable the feature before pushes are reviewed. After that, the scan runs automatically against connected repositories.
The resulting record links a vulnerability to the exact environment, branch and commit where it appeared. Pull request comments put the finding beside the proposed code, while the dashboard provides a central list across projects. CLI access gives developers another route to inspect findings without opening the dashboard.
Frequently asked questions
What is Vercel Security Review?
Vercel Security Review is a Vercel Agent capability that scans every push to a connected GitHub repository for vulnerabilities. It reports findings through pull request comments, the Security dashboard and the CLI, and can validate and push fixes with permission.
Which Vercel plan includes Security Review?
The public beta is available to Pro and Enterprise teams. The sources do not state whether it carries an additional charge.
Does Vercel Security Review scan direct production pushes?
Yes. Reviews start from GitHub push events, so direct and force pushes to production branches are included, not only changes submitted through pull requests.
Sources
3 checkedHow we cover tool news: Create With's tool desk drafts these reports with AI from the sources listed above and checks them against those sources before publishing.



 Framer